Offline signatures work without internet, detected apps can be uninstalled from the results screen, quarantine is verified, and there are far fewer false positives. New privacy controls let you withdraw consent and delete your data in Settings. Redesigned dashboard and faster startup.
Android app · Mobile security
Vipera: Mobile Security
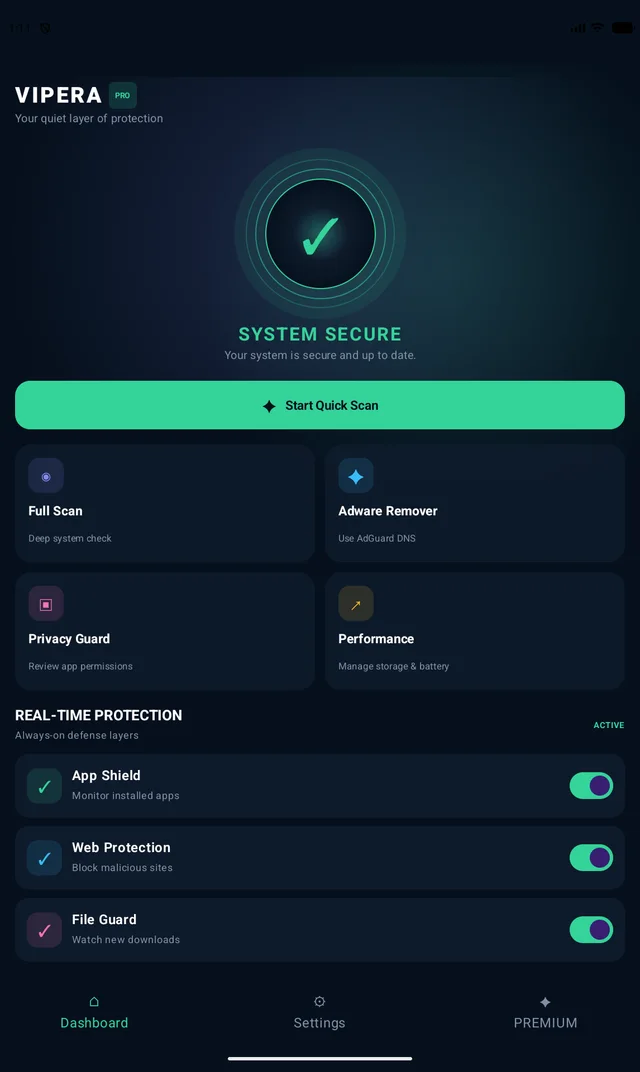
Vipera is an Android malware scanner from BlankCanvas Software. It checks APK files and installed apps against threat-intelligence databases and its own offline signatures by looking up each file’s SHA-256 hash, so the file itself never leaves your phone. No account or sign-up is needed.
4.9 (18 ratings) on Google Play · free to download · ads in the free version · Premium subscription · updated 10 Oct 2026
Under the hood
How Vipera checks files
Four steps, from a file on your phone to a result you can act on.
-
01
Hash the file on your phone
Vipera computes the SHA-256 hash of each APK file it scans. Known-bad hashes, and the industry-standard EICAR test file, are detected offline without an internet connection.
-
02
Look up the hash
Only the hash is sent to Vipera’s server, which checks MalwareBazaar, YARAify and ThreatFox. Premium adds AlienVault OTX, MetaDefender and an NVIDIA AI review.
-
03
Report only what’s confirmed
A file is reported as malicious only when a threat database or an exact offline signature identifies it. Weak signals are shown as “flagged for review” and are never removed automatically.
-
04
Remove it safely
Infected files move to quarantine in app-private storage with one tap, and can be restored or deleted later. Infected apps can be uninstalled straight from the results screen.
Pricing
Free vs Premium
Quick scans are free. Premium is a subscription managed in Google Play, and you can cancel it at any time.
| Feature | Free | Premium |
|---|---|---|
| Quick scanAPK files that are new or changed since the last scan | Yes | Yes |
| Full scanEvery APK file in your storage | No | Yes |
| Deep scanInstalled apps, plus risky combinations such as overlay and accessibility abuse | Once, after a short ad | Yes |
| Threat engines | MalwareBazaar, YARAify, ThreatFox | Adds AlienVault OTX, MetaDefender and an NVIDIA AI review |
| Automatic scheduled scans | No | Yes |
| Daily lookup limit | Standard | Higher |
| Ads | Yes | No |
Also in the app: App Shield, which checks new installs; a link checker using URLhaus and Google Safe Browsing; a breach monitor; a Wi-Fi security check; Photo Vault; Call Guard; a junk cleaner; and anti-theft tools.
Privacy
Privacy, in plain words
- Sent to the server: a file’s SHA-256 hash, never the file itself.
- Stored: hashes are kept with an anonymous account for up to 90 days. You can withdraw consent or delete this data at any time in Settings.
- Ads: the free version shows ads. The data-safety section on Google Play lists what the app and its ads collect and share.
- No sign-up: Vipera doesn’t ask for an account or an email address.
Honesty
Limits
Vipera works alongside Google Play Protect; it doesn’t replace it. No antivirus can detect every threat. Vipera reports a file as malicious only when a threat database or an exact offline signature identifies it, so brand-new malware that no database knows about yet can go unreported. Read a clean result as “nothing known was found”, not as a guarantee.
Updates
What’s new
FAQ
Vipera, answered.
Does Vipera upload my files?
No. Vipera sends only a file’s SHA-256 hash to its server, which checks it against MalwareBazaar, YARAify and ThreatFox; the file itself never leaves your phone. Hashes are kept with an anonymous ID for up to 90 days, and you can delete them in the app’s Settings.
Is Vipera free?
Yes. Vipera is free to download and quick scans are free, with ads in the free version. Premium, a subscription managed in Google Play, adds full and deep scans, automatic scheduled scans, three extra threat engines and a higher daily lookup limit.
Is Vipera the same as VIPRE?
No. Vipera: Mobile Security is an independent Android app made by BlankCanvas Software, the studio of Om Israni in Tenerife, Spain. It is not related to VIPRE Security or to Vipera plc, and it is published on Google Play under the developer name BlankCanvas Software.
Does Vipera replace Google Play Protect?
No. Vipera works alongside Google Play Protect. It adds SHA-256 lookups against public threat-intelligence databases and its own offline signatures, and it reports a file as malicious only when a database or an exact signature identifies it.
What happens when Vipera finds a threat?
Infected files move to quarantine in app-private storage with one tap and can be restored or deleted later. Infected apps can be uninstalled from the results screen; if an app blocks removal with device-admin rights, Vipera shows you how to revoke them. Weak signals are only flagged for review.
Support
Found a false positive
or a bug?
Email the app name and, if you can, the file’s SHA-256 hash. Messages come straight to the developer.